By Zahid Nawaz, Founder of Motion Graphix ·
Quick answer: Cybersecurity and compliance products are bought by people who are paid to be suspicious, so the explainer video has to behave differently. No fear-mongering, no padlock icons, no “in a world of rising threats”. The videos that work show the boring, specific task the product removes (the questionnaire, the audit evidence, the repeated ticket), prove it in the real interface, and state the certifications once, plainly, where they close deals. Below are eight examples, six from our security and compliance work and two from the public record, with the pattern each one gets right.
Why security videos are usually bad
Because they are written to scare the viewer, and the viewer is a CISO, a security engineer or a compliance lead who hears scare stories for a living. Dramatic music and a hooded figure at a keyboard signal that the vendor does not understand the buyer. The second failure is abstraction: “a unified platform for holistic risk visibility” describes nothing. Security buyers want to see the control working, the evidence being collected, the answer being reused. Specificity is the whole game. Our cybersecurity explainer video service is built around that; this article is about the videos.
8 cybersecurity and compliance explainer video examples
1. Sprinto Trust Center: one page instead of a hundred emails
A wall of buyer questions, then one page that answers all of them: posture, uptime and certifications, published rather than emailed. The video’s argument is the contrast between the inbox and the page. If your product replaces a repetitive process, show the repetition first.
2. Sprinto Trust Center (sales version): the same product inside a stalling deal
Same product, told from inside a deal that is going quiet. The buyer asks about GDPR and incident response, and the trust centre answers before the call ends. One product, two scripts for two audiences (security teams and sales teams), which is cheaper than one video that tries to speak to both.
3. Sprinto Security Questionnaires: show the hours disappearing
Every questionnaire asks the same things in a different order. The video shows past answers being reused, then the hours and the tooling cost that disappear with them. Compliance buyers respond to time and cost numbers more than to any security claim, because time and cost are what they are measured on.
4. AudioEye: the document that unblocks the deal
Accessibility documentation is the task teams put off until a deal depends on it. A presenter carries the why while the screen shows a VPAT being generated and exported. The structure, human for motivation and screen for proof, is the standard for compliance products, and the export at the end is the payoff.
5. SuperOps: let the repetition play out
The same VPN ticket, twice a week, forever. The video lets that repetition play out on camera, then hands it to the AI agent. For IT operations and security tooling, boredom is the enemy you are selling against, so make the viewer feel the boredom for five seconds before you relieve it.
6. Novu: the surface and the switchboard
Notifications are infrastructure, so the video shows the surface users see and the switchboard behind it: in-app, email, SMS and push from one place. Security and infrastructure products need this two-layer view. Show what the end user experiences for two seconds, then live in the console where your buyer works.
7. Public example: explaining security to non-technical decision makers
Among publicly available videos, the ones that explain security for local government and other non-specialist audiences succeed by defining terms (assets, information security, incident) in plain language and tying each to a decision the viewer actually makes. If your buyer includes a board or a budget holder who is not technical, make a separate video for them. Do not water down the engineer’s video.
8. Public example: the enterprise threat platform that shows the console
The better enterprise security explainers from large vendors spend most of their runtime in the actual product, with threat data on screen and a clear sequence of detect, investigate, respond. The weaker ones are three minutes of stock footage and a logo. The difference is whether the viewer can tell what the product looks like at the end.
Patterns across the ones that worked
- The task, not the threat. Questionnaires, evidence collection, tickets, VPATs, access reviews. Security buyers are sold by the work that goes away.
- Real interface, real data shapes. Synthetic but realistic: plausible control names, plausible asset counts, plausible timestamps. Lorem ipsum in a security console destroys credibility instantly.
- Certifications stated once, at the end. SOC 2, ISO 27001, HIPAA, GDPR, on screen, where they close deals. Not as the opening hook.
- Calm pacing, dark UI, no drama. The product should look like something a security engineer would be happy to have on a second monitor.
- Two audiences, two videos. One for the practitioner who will use it, one for the executive who will approve it. Sprinto’s two trust-centre scripts are the model.
Style choices for security and compliance
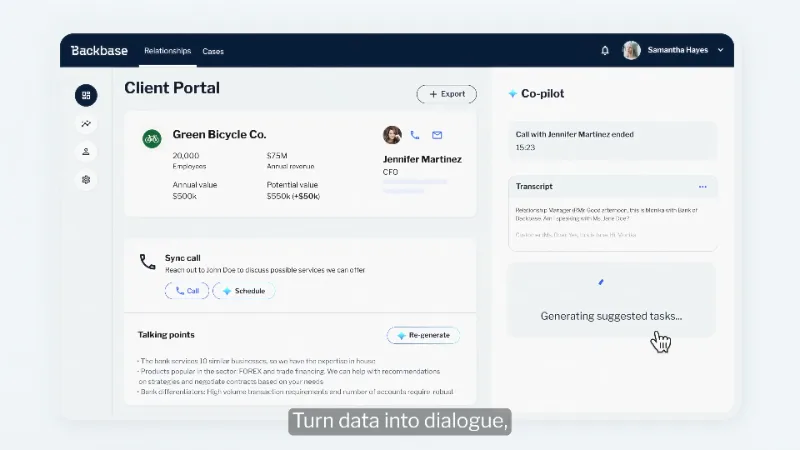
UI-led animation for anything with a console. Isometric for network and infrastructure views where several systems need to appear at once; see when isometric works. A presenter for the trust layer: a real person from the company saying the certifications out loud carries weight with a buyer whose job is to assess vendors. What to avoid: padlocks, shields, binary rain, hooded hackers, red alert pulses. All of them say “we are generic”. For the full range of options, explainer video styles compared.
Cost and review
Security and compliance videos go through more review than most: legal, security and sometimes a certification body’s wording rules. We lock all claims at script stage and keep two revision rounds at every stage, which has been enough for every compliance client so far. The price is a flat $1,450 including script, storyboard, animation, a human voice-over, social and ad cuts, source files and 90 days of changes, which security teams tend to use when a certification is renewed and the end card needs updating.
Quick questions
How long should a cybersecurity explainer video be?
60 to 90 seconds for the website and events. A two to four minute walkthrough for security reviewers who want to see the full workflow before a trial.
Should we mention specific threats or breaches?
Rarely. Your buyer knows the threat landscape better than your video does. Name the task you remove instead.
Can we show our real console?
Yes, with synthetic data built to look like a real environment. Never real customer or asset data.
Where can we see these videos?
Our six are in the portfolio and on the cybersecurity page.